The other day we were at a client site doing a penetration test. This was a very big deployment with almost 1000 routers. At some point during the test we managed to get the read/write community string of one of the routers, as there was a script with the hard-coded credentials.
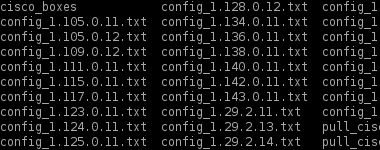
We managed to connect to the router with the SNMP credentials and pulled the Cisco config file. After that, we decoded the telnet and enable passwords and we were ready to go. We tried (with no much hope initially) a couple of other routers reusing the telnet password and they all worked. Every single router was protected with exactly the same password.
We had limited time and the prospect of telneting 1000 routers pulling config files was not very appealing so we wrote a nice python script to pull them for us. We released the tool in our research section, so check it out if you are interested.
The lesson learnt here is that no matter how confident you are about the strength of your password because it can be potentially compromised and if you are reusing it, the impact for the business becomes critical.