Intelligence-led resilience testing for the UK’s critical national infrastructure.
Realistic attack simulation that UK regulators expect, with support before, during and after the engagement.
Our TBEST threat-led penetration testing helps you meet the regulator’s requirements and tests your resilience against real attacks facing the UK telecommunications industry.
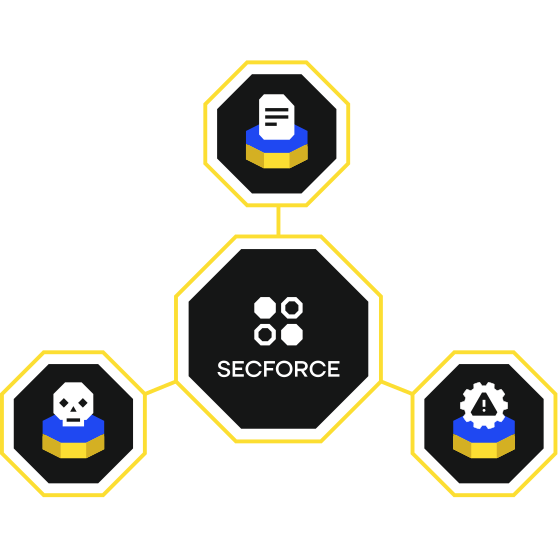

SECFORCE is a CREST-accredited and TBEST-approved Penetration Test Service Provider (PTSP). Our consultants hold CCRTS (CREST Certified Red Team Specialist) qualifications, and all our TBEST engagements are managed by a CCRTM (CREST Certified Red Team Manager).

We work with long-standing, trusted, and accredited Threat Intelligence (TI) partners. We can also engage with any TI provider you or the regulator chooses. Our Red Team participates actively throughout the TI phase (which precedes testing), so scenarios stay grounded in your real threat landscape and flow seamlessly into testing.

Our consultants have safely tested complex, large-scale infrastructure, including industry-critical telecoms operators with bespoke and proprietary network protocols.

Our attack simulations are conducted under strict controls, with detailed test plans (including contingencies and communication protocols) and continuous involvement from the White Team. We’re also ISO 27001 and SOC 2 certified.

All our TBEST simulations reflect the current tactics, techniques, and procedures of threat actors relevant to UK telecoms, rather than generic testing scenarios. We are a specialist red team operator with a dedicated R&D function and a proprietary offensive framework developed in-house.

Tailored to TBEST, our reporting includes executive-level insights, technical detail, and practical remediation guidance. We also provide retesting support and are there for our clients before, during, and after the engagement. We help turn findings into meaningful improvements in your security posture.
TBEST (Telecom BEST) is the UK government’s threat-led penetration testing framework for the telecommunications sector, mirroring the CBEST model applied to systemically critical telecoms providers.
Overseen by the Department for Science, Innovation and Technology (DSIT) and delivered in partnership with CREST, TBEST is designed to assess the cyber
resilience of the UK’s most critical communications infrastructure against the threat actors most likely to target it.
Like CBEST, TBEST is intelligence-driven, with bespoke Threat Intelligence used to develop realistic attack scenarios tailored to the specific threat profile of the target organisation.
| TBEST Requirement | SECFORCE |
|---|---|
| CREST-accredited |  |
| Approved under the TBEST scheme | |
| CCRTS (CREST Certified Red Team Specialist) Consultants | |
| CCRTM (CREST Certified Red Team Manager) Consultants | |
The assessment is launched, the scope is agreed, and the TI and PTSP are engaged.
A TBEST-certified TISP gathers intelligence on the organisation’s threat landscape and develops realistic attack scenarios.
A TBEST-certified PTSP tests the organisation’s critical systems and functions through intelligence-led attack simulation.
Findings are turned into a formal action plan, which the regulator reviews and supervises until the agreed-upon remediation activities have been completed.
If your operations extend beyond the UK telecoms sector, TBEST may be only one of the frameworks you need to satisfy.
We can help there, too. Our team has completed dozens of engagements under the other major Threat-Led Penetration Testing (TLPT) frameworks, including CBEST, TIBER-EU, DORA TLPT, iCAST and CORIE.
Among them were some of the first engagements in the world spanning multiple frameworks and jurisdictions, including combined CBEST and TIBER exercises.
Thank you!
Please try again later.

